Audit AI agents with Nvidia's safety platform
Security consultants can offer audits for autonomous AI agents using Nvidia's new open safety framework.
Open NuviFlux for the evidence, open questions, and first test.
THE OPPORTUNITY, IN CONTEXT
Security reviews for AI agent permissions
The business model
Giving an AI agent access to company systems raises a practical question: how much access is too much? A security consultant could offer a review of agent permissions, runtime policies, and audit evidence, with findings the engineering team can understand.
What has been observed
NVIDIA's Open Agent Safety Platform combines the OpenShell software runtime with an optional Sentry hardware layer. Published OpenShell documentation covers access controls and audit logs. Those resources support technical evaluation; they do not establish demand for an independent consulting service.
Entry conditions and costs
The work requires security expertise, an authorized environment, and time to interpret evidence. Hardware access depends on the review's scope. Log gaps and permissive policies can limit the conclusions, and a platform review is not a guarantee that an agent is safe.
The key question
Would a team pay for a clear assessment of its agent controls beyond what its own engineers can provide?
Common questions
Does an OpenShell review include Sentry hardware testing?
Only if that layer is explicitly included and available. A software review does not validate BlueField-based enforcement or quarantine speed.
Is an audit log a finished client report?
No. Logs provide evidence. Findings need context, an explanation of coverage and gaps, and professional interpretation.
A CLOSER LOOK
Understanding an agent's access
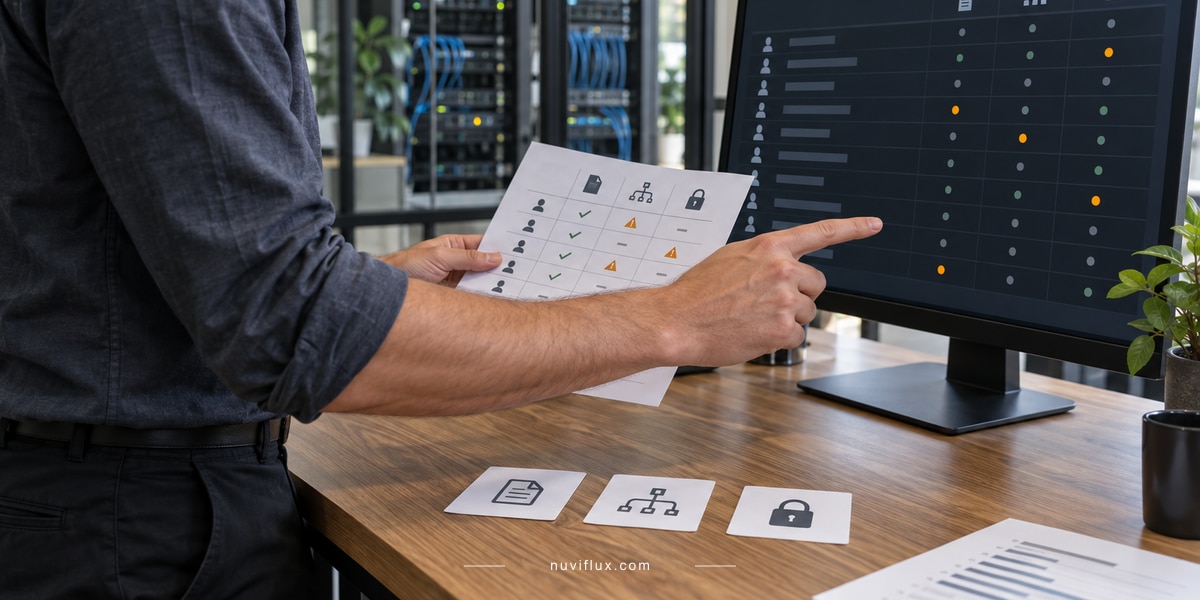
Teams deploying AI agents need to understand what those agents can access. A consultant could review OpenShell policies and audit evidence to help explain gaps in their controls.